#include <borked_blowfish_crypto.h>
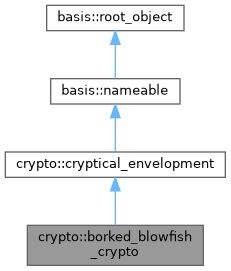
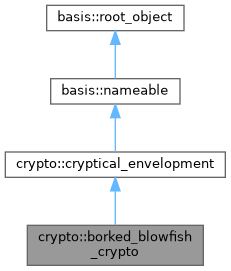
Public Member Functions | |
| borked_blowfish_crypto (int key_size) | |
| this will create a new random key of the "key_size", in bits. | |
| borked_blowfish_crypto (const basis::byte_array &key, int key_size) | |
| uses a pre-existing "key". | |
| borked_blowfish_crypto (const borked_blowfish_crypto &to_copy) | |
| copy constructor. | |
| virtual | ~borked_blowfish_crypto () |
| borked_blowfish_crypto & | operator= (const borked_blowfish_crypto &to_copy) |
| DEFINE_CLASS_NAME ("borked_blowfish_crypto") | |
| virtual int | minimum_key_size_in_bits () const |
| returns the minimum key size in bits supported here. | |
| virtual int | maximum_key_size_in_bits () const |
| returns the maximum key size in bits supported here. | |
 Public Member Functions inherited from crypto::cryptical_envelopment | |
| cryptical_envelopment (const EVP_CIPHER *cipher_type) | |
| constructor requires the type of encryption to use. | |
| cryptical_envelopment (const cryptical_envelopment &to_copy) | |
| copy constructor. | |
| virtual | ~cryptical_envelopment () |
| cryptical_envelopment & | operator= (const cryptical_envelopment &to_copy) |
| bool | set_key (int key_size) |
| this will create a new random key of the "key_size", in bits. | |
| bool | set_key (const basis::byte_array &new_key, int key_size) |
| sets the encryption key to "new_key" with a "key_size" in bits. | |
| DEFINE_CLASS_NAME ("cryptical_envelopment") | |
| int | key_size () const |
| const basis::byte_array & | get_key () const |
| returns our current key. | |
| bool | generate_key (int size, basis::byte_array &new_key) |
| creates a "new_key" of the "size" (in bits) specified. | |
| bool | encrypt (const basis::byte_array &source, basis::byte_array &target) const |
| encrypts the "source" array into the "target" array. | |
| bool | decrypt (const basis::byte_array &source, basis::byte_array &target) const |
| decrypts the "target" array from the encrypted "source" array. | |
| Public Member Functions inherited from basis::nameable | |
| virtual const char * | class_name () const =0 |
| Returns the bare name of this class as a constant character pointer. | |
Static Public Member Functions | |
| static int | static_minimum_key_size_in_bits () |
| static int | static_maximum_key_size_in_bits () |
| Static Public Member Functions inherited from crypto::cryptical_envelopment | |
| static const basis::byte_array & | init_vector () |
| returns the initialization vector that is used by this class. | |
Detailed Description
Definition at line 32 of file borked_blowfish_crypto.h.
Constructor & Destructor Documentation
◆ borked_blowfish_crypto() [1/3]
| crypto::borked_blowfish_crypto::borked_blowfish_crypto | ( | int | key_size | ) |
this will create a new random key of the "key_size", in bits.
the valid published sizes are from 32 bits to 448 bits, but openssl borks with lower than 128 seemingly. so we are forcing a higher minimum here than the published algorithm. keys of 168 bits and larger should be very secure. it is said (ed: by who?) that if a billion computers each tried a billion keys a second, then a 168 bit key would take 10 * 10^24 years to break (using brute force). this would be essentially unbreakable since the age of the universe is only 10 * 10^9 years so far. (estimates not guaranteed.)
Definition at line 46 of file borked_blowfish_crypto.cpp.
References crypto::cryptical_envelopment::key_size(), and crypto::cryptical_envelopment::set_key().
◆ borked_blowfish_crypto() [2/3]
| crypto::borked_blowfish_crypto::borked_blowfish_crypto | ( | const basis::byte_array & | key, |
| int | key_size | ||
| ) |
uses a pre-existing "key".
Definition at line 52 of file borked_blowfish_crypto.cpp.
References crypto::cryptical_envelopment::key_size(), and crypto::cryptical_envelopment::set_key().
◆ borked_blowfish_crypto() [3/3]
| crypto::borked_blowfish_crypto::borked_blowfish_crypto | ( | const borked_blowfish_crypto & | to_copy | ) |
copy constructor.
Definition at line 58 of file borked_blowfish_crypto.cpp.
◆ ~borked_blowfish_crypto()
|
virtual |
Definition at line 64 of file borked_blowfish_crypto.cpp.
Member Function Documentation
◆ DEFINE_CLASS_NAME()
| crypto::borked_blowfish_crypto::DEFINE_CLASS_NAME | ( | "borked_blowfish_crypto" | ) |
◆ maximum_key_size_in_bits()
|
inlinevirtual |
returns the maximum key size in bits supported here.
Implements crypto::cryptical_envelopment.
Definition at line 59 of file borked_blowfish_crypto.h.
References static_maximum_key_size_in_bits().
◆ minimum_key_size_in_bits()
|
inlinevirtual |
returns the minimum key size in bits supported here.
Implements crypto::cryptical_envelopment.
Definition at line 58 of file borked_blowfish_crypto.h.
References static_minimum_key_size_in_bits().
◆ operator=()
| borked_blowfish_crypto & crypto::borked_blowfish_crypto::operator= | ( | const borked_blowfish_crypto & | to_copy | ) |
Definition at line 68 of file borked_blowfish_crypto.cpp.
◆ static_maximum_key_size_in_bits()
|
inlinestatic |
Definition at line 62 of file borked_blowfish_crypto.h.
Referenced by maximum_key_size_in_bits().
◆ static_minimum_key_size_in_bits()
|
inlinestatic |
Definition at line 60 of file borked_blowfish_crypto.h.
Referenced by minimum_key_size_in_bits().
The documentation for this class was generated from the following files:
- /opt/feistymeow.org/feisty_meow/nucleus/library/crypto/borked_blowfish_crypto.h
- /opt/feistymeow.org/feisty_meow/nucleus/library/crypto/borked_blowfish_crypto.cpp
